
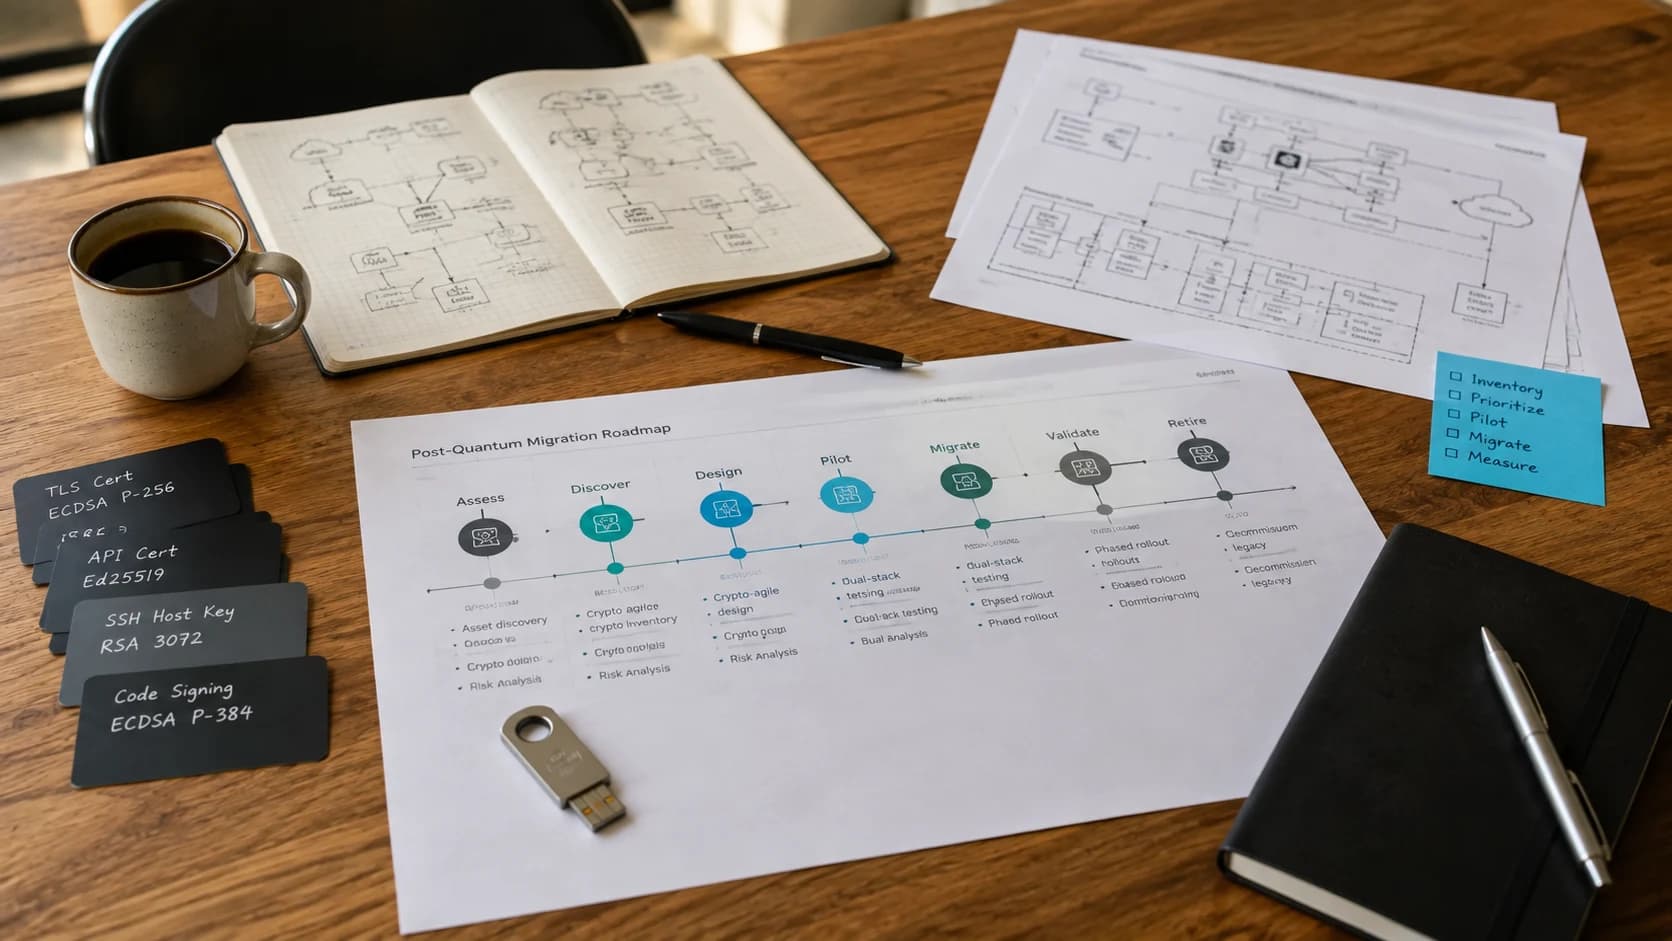
A Practical Post-Quantum Cryptography Migration Roadmap
Post-quantum migration is an inventory and dependency program before it becomes an algorithm rollout. Organizations need to find where public-key cryptography protects long-lived data, authentication, software signatures, certificates, network protocols, hardware, and third-party services.
NIST finalized FIPS 203, 204, and 205 in August 2024 and encouraged administrators to begin transitioning. Starting now matters because product support, protocol changes, interoperability tests, and replacement cycles can take years.
Prioritize by data lifetime and replacement difficulty
Begin with data that must remain confidential for many years and could be collected now for later decryption. Then identify systems with long procurement cycles, embedded cryptography, hard-coded algorithms, fixed hardware, or vendors without a documented roadmap.
A cryptographic inventory should record algorithm, key size, purpose, owner, product, protocol, data protected, certificate authority, dependency, and upgrade path. Discovery tools help, but contracts, architecture diagrams, code search, and vendor questions remain necessary.
- Separate key establishment, encryption, and digital-signature use cases.
- Prefer crypto-agile designs that can change algorithms without replacing the entire system.
- Test performance, message size, compatibility, rollback, and monitoring.
- Do not invent custom cryptography or treat experimental support as production readiness.
Move through governed pilots
Select a bounded service with a cooperative vendor, observable traffic, and a reversible change. Establish success criteria, test hybrid or post-quantum options supported by the product, and record interoperability failures. Feed the result into procurement standards and architecture patterns.
Governance should track unsupported products, vendor commitments, certificate and protocol dependencies, budget cycles, and migration risk. The outcome is not a one-time conversion but the ability to adapt cryptography as standards and products evolve.
Put the lesson into practice
- Assign an owner for cryptographic discovery and migration.
- Inventory long-lived data and hard-to-replace systems first.
- Request product-specific PQC roadmaps from strategic vendors.
- Pilot supported standards in a reversible, measurable service.
- Add crypto-agility and migration evidence to architecture reviews.
Related Outfaze guidance
- Vulnerability assessment
- Compliance as a Service
- Cloud security monitoring
- Penetration testing
- Outfaze cybersecurity services