
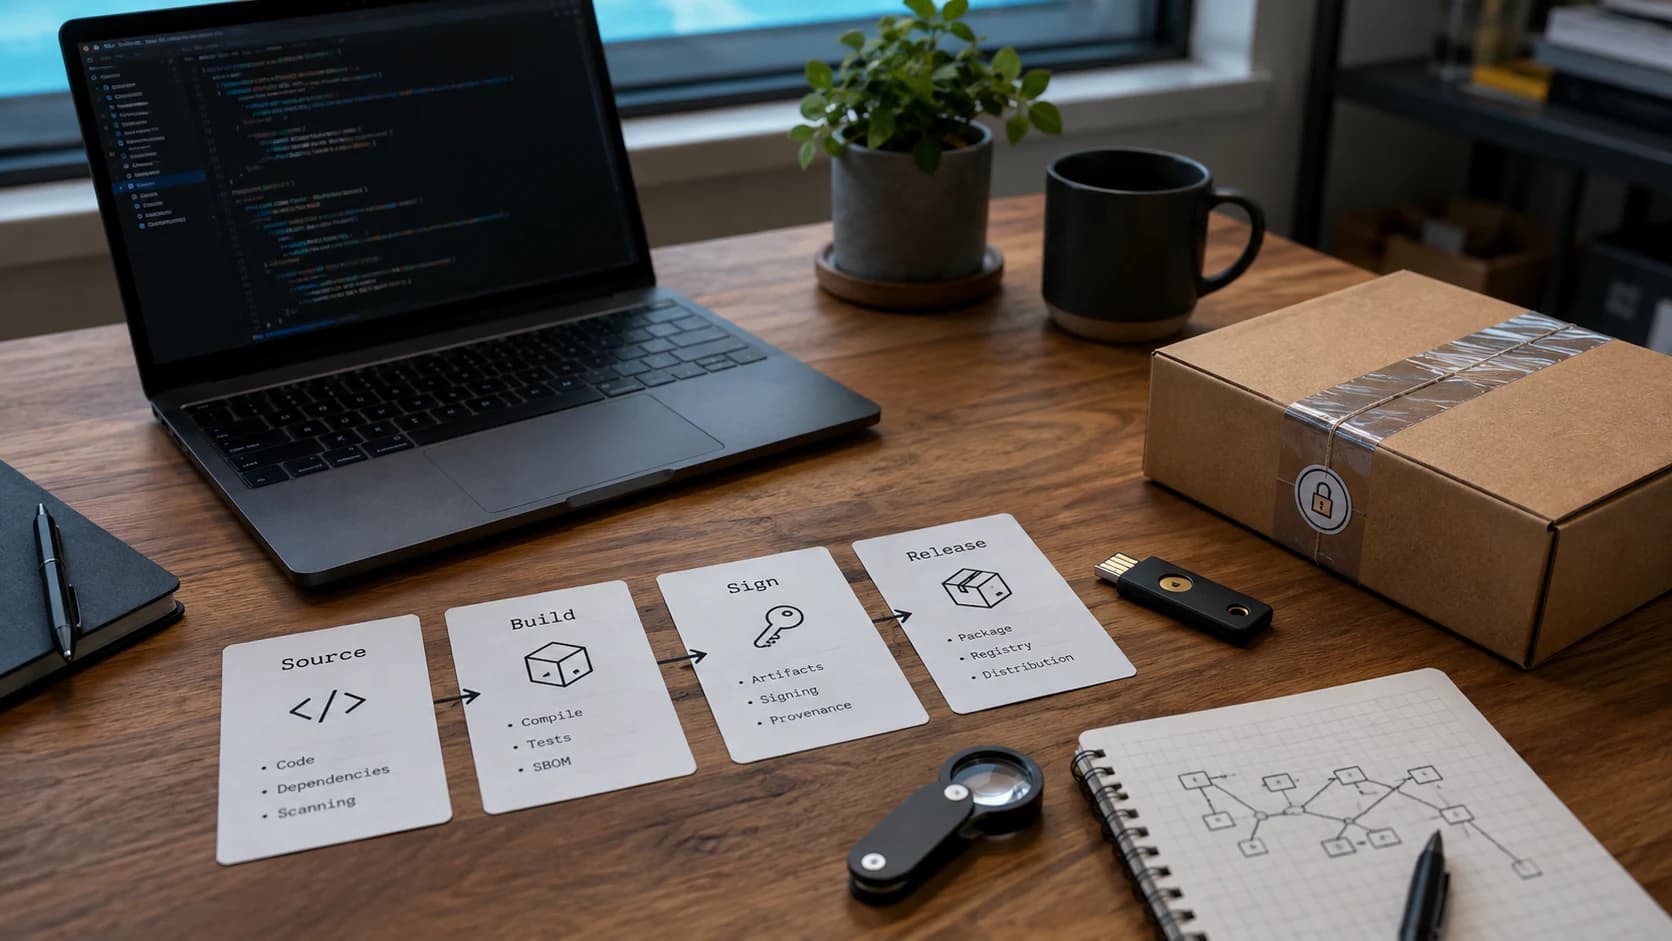
Software Supply Chain Security Controls That Matter
Software supply chain security covers more than third-party libraries. Source control, developer identities, build runners, package registries, signing keys, release channels, deployment automation, and the vendors behind them can each alter what reaches production.
SolarWinds, Kaseya, 3CX, Log4Shell, and XZ Utils were different incidents, but each challenged the assumption that trusted software or a normal update should be allowed to operate without independent verification and monitoring.
Start with the paths that can change production
Map who and what can merge code, change build definitions, publish packages, sign releases, modify deployment secrets, or bypass normal approval. Protect those paths with phishing-resistant authentication, short-lived credentials, separation of duties, reviewed changes, and logs stored outside the system being administered.
An SBOM can improve component visibility, but it is not a complete control. Teams also need to know where a component is deployed, whether the vulnerable function is reachable, who owns the application, and how quickly a safe release can be tested and delivered.
- Pin and verify dependencies where the ecosystem supports it.
- Isolate build systems and minimize their standing credentials.
- Protect signing keys with restricted, auditable workflows.
- Monitor released software for unexpected network and child-process behavior.
Ask suppliers for evidence you can use
Procurement should establish notification routes, vulnerability handling, supported versions, secure update mechanisms, logging capabilities, subcontractor dependencies, and end-of-life obligations. The aim is not a questionnaire score. It is to learn how the supplier will help you detect, contain, and recover from a compromise.
Prepare an emergency process for disabling an update channel, revoking a package, blocking indicators, identifying deployed versions, and contacting affected customers. Supply-chain response becomes slower when ownership is first discussed after public disclosure.
Put the lesson into practice
- Inventory the systems that can modify or release production code.
- Require strong authentication and least privilege on each control point.
- Connect component data to deployment and ownership records.
- Define supplier-notification and emergency-update procedures.
- Exercise one compromised dependency or build-runner scenario.
Related Outfaze guidance
- Vulnerability assessment
- Patch management
- Managed detection and response
- Penetration testing
- Compliance as a Service