 Outfaze Security Team
GRU Logistics Targeting: Practical Defense Lessons
Turn the 2025 joint advisory on Russian GRU targeting of logistics and technology organizations into concrete exposure, identity, and monitoring work.
Read guide
Outfaze insights / Page 3
Clear priorities. Practical protection. A partner accountable for the next step.
Practical field guides for operating teams working through incident readiness, security operations, cloud monitoring, vulnerability management, and service delivery.
Archive / Page 3
Explore practical guidance for MSPs, small IT teams, and security leaders responsible for improving protection without adding noise.
Showing 21–30 of 56 insights
 Outfaze Security Team
Turn the 2025 joint advisory on Russian GRU targeting of logistics and technology organizations into concrete exposure, identity, and monitoring work.
 Outfaze Security Team
Understand how managed detection and response differs from SOC as a service, what each model is responsible for, and how to evaluate the right fit.
 Outfaze Security Team
Use the 2025 joint advisory on Medusa ransomware to strengthen identity controls, external exposure, detection, segmentation, and recovery readiness.
 Outfaze Security Team
Understand Storm-2372 device code phishing and reduce token theft with flow restrictions, sign-in monitoring, user verification, and containment.
 Outfaze Security Team
A practical incident response framework for small IT teams, from defining roles and escalation paths to preserving evidence and rehearsing recovery.
 Outfaze Security Team
The July 2024 Windows outage showed why security tooling needs staged change, recovery access, dependency mapping, and tested continuity plans.
 Outfaze Security Team
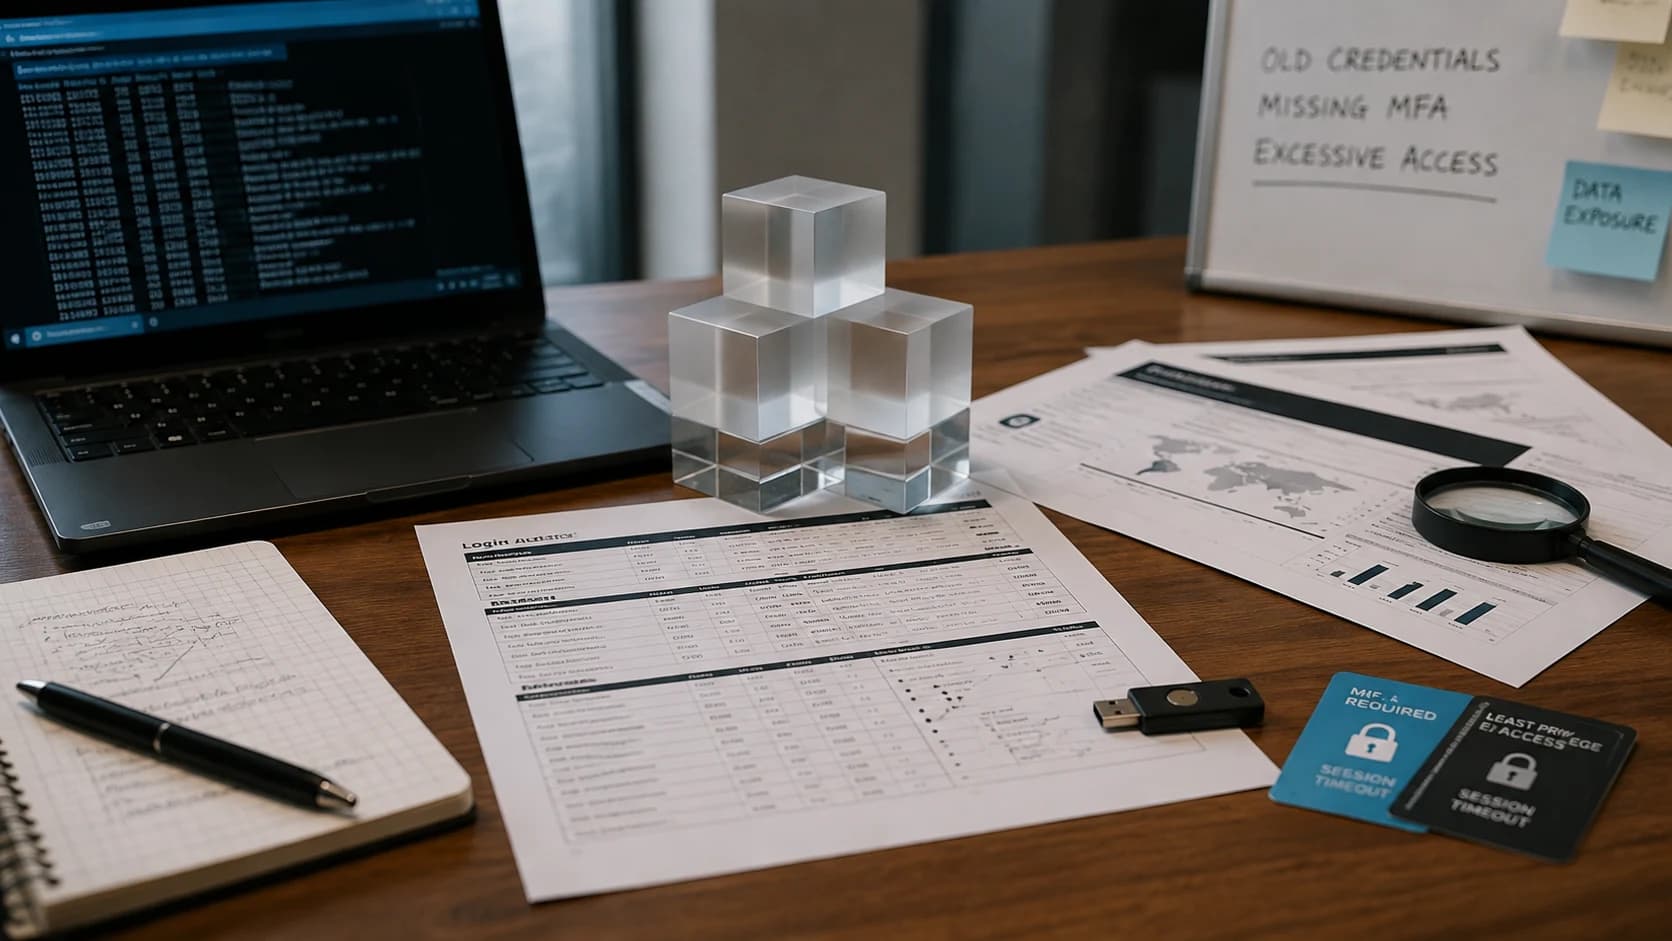
The UNC5537 campaign shows how old infostealer credentials, missing MFA, and weak network policy can expose high-value cloud data stores.
 Outfaze Security Team
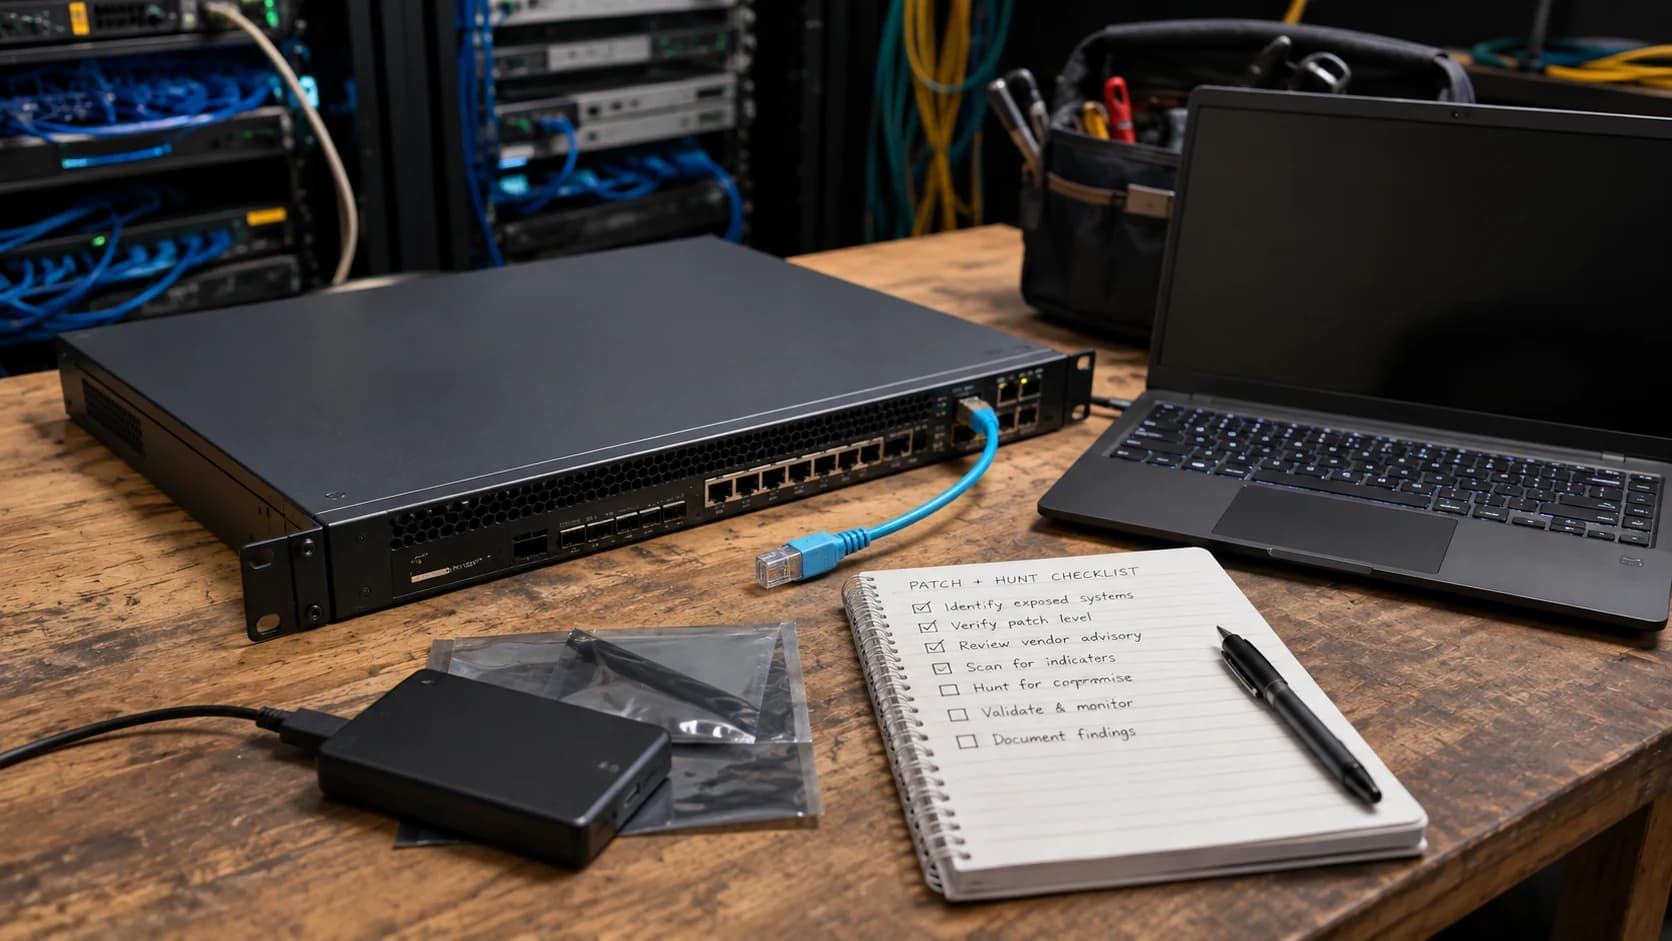
A response guide for the actively exploited PAN-OS GlobalProtect command injection flaw, from exposure checks to patching and incident scoping.
 Outfaze Security Team
The XZ Utils backdoor exposed trust risks in open-source maintenance, build pipelines, dependency visibility, and rapid containment decisions.
 Outfaze Security Team
The Change Healthcare disruption illustrates how concentrated service dependencies can turn a cyber incident into a sector-wide continuity crisis.
Tell us what you need to protect. We’ll help define a practical starting point around your environment, team, and priorities.