 Outfaze Security Team
Software Supply Chain Security Controls That Matter
A practical guide to software supply chain security across dependencies, build systems, release integrity, vendor evidence, and incident response.
Read guide
Outfaze insights / Page 2
Clear priorities. Practical protection. A partner accountable for the next step.
Practical field guides for operating teams working through incident readiness, security operations, cloud monitoring, vulnerability management, and service delivery.
Archive / Page 2
Explore practical guidance for MSPs, small IT teams, and security leaders responsible for improving protection without adding noise.
Showing 11–20 of 56 insights
 Outfaze Security Team
A practical guide to software supply chain security across dependencies, build systems, release integrity, vendor evidence, and incident response.
 Outfaze Security Team
Understand how automated device code phishing abuses legitimate sign-in flows and how defenders can restrict, detect, and contain token theft.
 Outfaze Security Team
Translate NIST SP 800-61 Rev. 3 into an incident response operating model spanning preparation, detection, response, recovery, and improvement.
 Outfaze Security Team
Create a defensible SaaS offboarding process covering identities, sessions, tokens, devices, shared credentials, data ownership, and verification.
 Outfaze Security Team
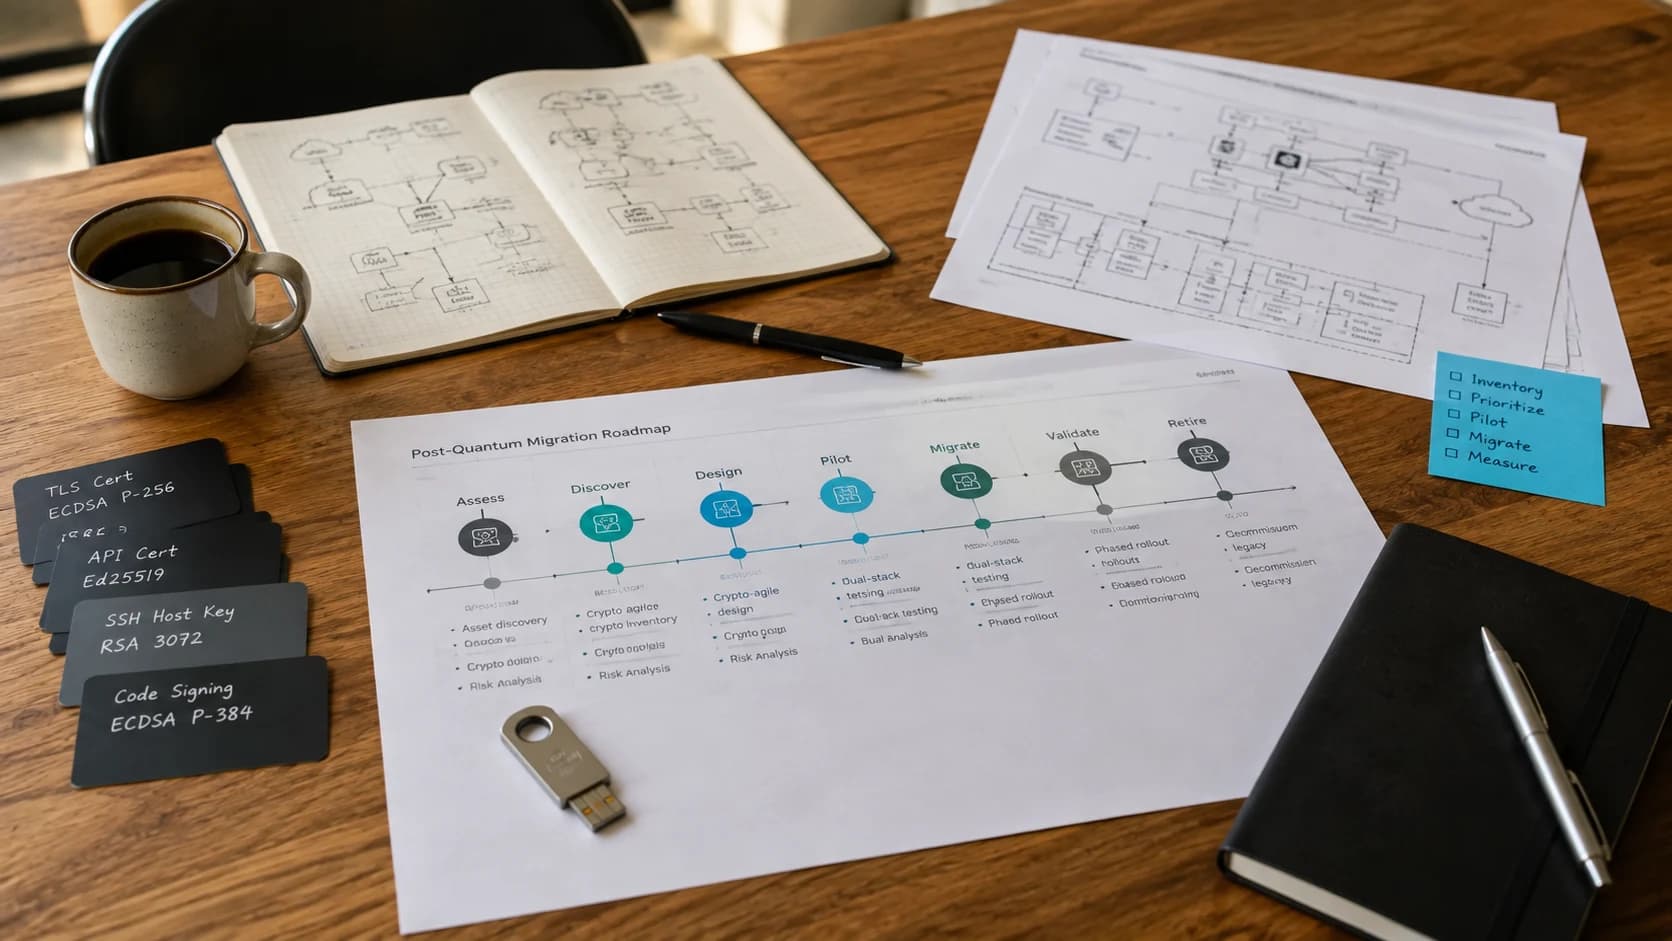
Start post-quantum migration with cryptographic discovery, data-life analysis, vendor planning, crypto-agility, pilots, and accountable governance.
 Outfaze Security Team
A practical guide to prioritizing cloud identity, control-plane, data, network, and logging signals without overwhelming the security team.
 Outfaze Security Team
A due-diligence guide for MSPs evaluating cybersecurity partners across service scope, escalation, evidence, tenant operations, and customer ownership.
 Outfaze Security Team
Respond to active ToolShell exploitation of on-premises SharePoint by patching supported servers, rotating machine keys, hunting, and scoping exposure.
 Outfaze Security Team
Move beyond periodic scanning with a repeatable vulnerability management lifecycle for asset coverage, validation, prioritization, remediation, and reporting.
 Outfaze Security Team
Learn how vishing campaigns trick users into authorizing malicious connected apps and how to govern OAuth access, monitoring, and response.
Tell us what you need to protect. We’ll help define a practical starting point around your environment, team, and priorities.